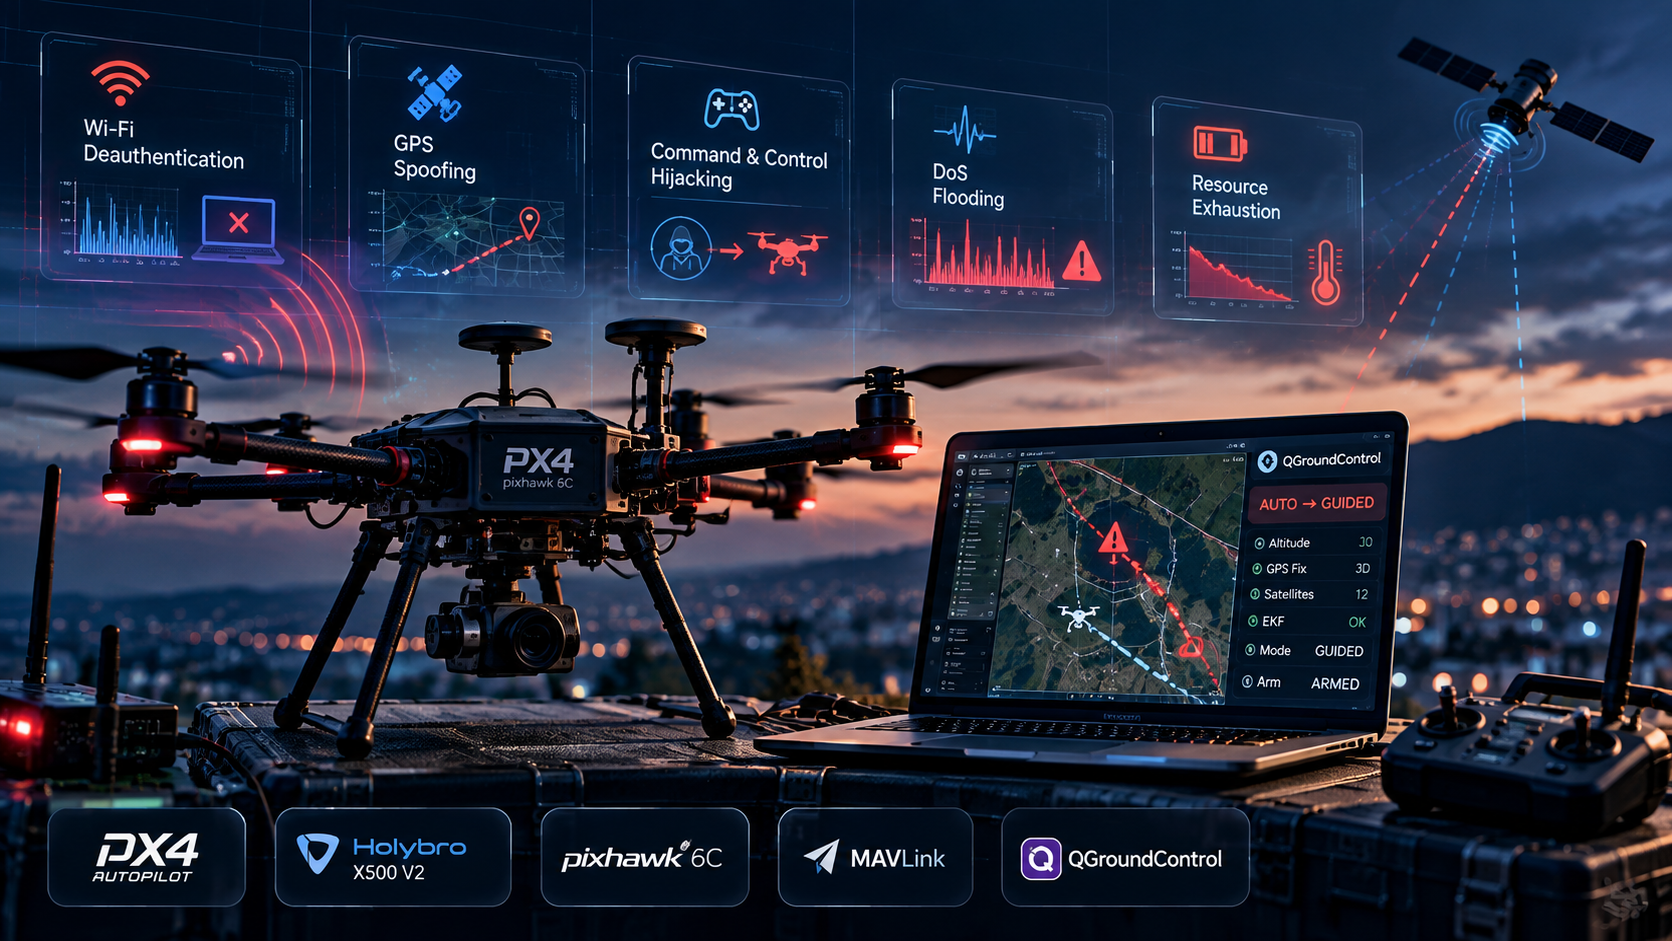
Penetration Testing Framework for UAV Networks
Designed and executed a reproducible UAV penetration-testing framework on a PX4 Holybro X500 V2 / Pixhawk 6C platform. Evaluated Wi‑Fi deauthentication, GPS spoofing, MAVLink C2 hijacking, DoS flooding, and battery/resource exhaustion using unified metrics: disruption latency, recovery time, path deviation, CPU/MCU load, and operational continuity. Delivered cross‑attack benchmarks, CIA impact mapping, and practical hardening priorities for UAV operators.
Falcon-Style EDR Detection & Automated Containment Lab
Built a Falcon-style EDR lab using Wazuh and Sysmon to detect PowerShell abuse, reconnaissance, and multi-stage attacks with automated host isolation.
Web Application Firewall (WAF) Security Lab
Deployed ModSecurity with OWASP CRS to protect DVWA from SQL injection, XSS, brute-force, and command injection attacks with Splunk-based monitoring.
Active Directory Ransomware Detection Lab
Simulated a ransomware attack in an Active Directory lab using Kali Linux, Impacket, Snort, and Splunk to detect lateral movement, PowerShell abuse, and file encryption activity.
IoT Network Exploitation & MQTT Security Lab
Performed IoT host discovery, MQTT MiTM attacks, Philips Hue API exploitation, APK reverse engineering, and Wireshark traffic analysis to identify insecure services and exposed APIs.
ICS & Smart Device Threat Modeling Lab
Performed STRIDE and LINDDUN threat modeling on smart and industrial IoT systems to identify spoofing, tampering, privacy, and denial-of-service risks with secure design mitigations.
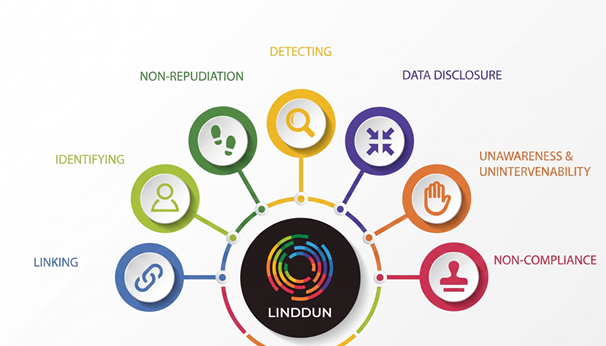
IoT Cloud Security & Privacy Threat Modeling
Analyzed IoT cloud security and privacy risks using STRIDE and LINDDUN threat models, with mitigations for spoofing, tampering, DoS, and data exposure in smart home devices.
From Water Plant to Swimming Pool: Full ICS Exploitation
Full ICS pentest: chained RDP, exposed CCTV, and plaintext credentials to access the engineering workstation. Modified PLC logic and disabled alarms.